Introduction
Every time you open an application, save a document, connect to the internet, or play a video on your computer, several processes work together behind the scenes to make it happen. While the interface of an operating system is what users interact with directly, the real coordination takes place at a deeper level. One of the most important components responsible for this work is the kernel.
The kernel is the core part of an operating system. It acts as a bridge between software applications and the computer’s hardware, managing resources such as the processor, memory, storage devices, and network connections. Without it, applications would have no reliable way to access hardware or share system resources safely.
Although users rarely interact with the kernel directly, its design has a major influence on a computer’s performance, stability, security, and compatibility. Different operating systems use different kernel architectures to balance these requirements.
For example, Linux uses a monolithic kernel design with extensive modular capabilities, while Windows and macOS use hybrid approaches that combine characteristics of different architectural models.
Understanding kernel architecture helps explain why operating systems behave differently, how applications communicate with hardware, and why some systems prioritize flexibility while others emphasize isolation or specialized performance.
In this article, we will explore what a kernel is, how it manages hardware and software, the major types of kernel architecture, and the advantages and limitations of each approach.
What Is a Kernel in an Operating System?
<AsyncImage query=”computer operating system kernel architecture diagram hardware kernel applications layered structure” aspectRatio=”16:9″ width=”100%”/>
A kernel is the central component of an operating system that manages access to hardware and coordinates essential system operations.
Applications such as web browsers, media players, games, and office programs depend on the kernel to perform tasks that require privileged access to the computer.
For example, when an application needs to read a file, the kernel coordinates the request with the appropriate filesystem and storage driver. When an application needs memory, the kernel helps allocate and protect the required memory space.
The kernel also ensures that multiple applications can share hardware resources without interfering unnecessarily with one another.
Why Is the Kernel Important?
Modern computers run many processes simultaneously. A browser may have multiple tabs open, a music player may be streaming audio, and an antivirus program may be scanning files in the background.
All these activities compete for limited resources.
The kernel helps manage these demands by deciding which processes receive processor time, which memory regions they can access, and how they communicate with devices.
Its responsibilities commonly include:
- Process management: Creating, scheduling, and ending processes and threads.
- Memory management: Allocating memory and isolating the memory spaces of different processes.
- Device management: Coordinating communication with hardware through device drivers.
- File and storage management: Providing core services that support filesystems and storage access.
- Security and permissions: Enforcing access controls and protecting privileged operations.
- System calls: Providing controlled entry points through which applications request operating system services.
- Interrupt handling: Responding to signals from hardware and other system events.
The precise responsibilities vary by operating system and kernel design, but these functions form the foundation of most general-purpose operating systems.
How Does a Kernel Work?
The kernel operates between applications and the hardware, but the relationship is more sophisticated than a simple communication channel.
Most modern operating systems separate execution into different privilege levels. Applications normally run with restricted privileges, while the kernel runs with the authority needed to manage protected resources.
This separation helps prevent ordinary applications from directly modifying critical system components.
User Mode and Kernel Mode
A typical operating system distinguishes between two important execution environments.
<box border radius=”xl” padding={3} gap={3}> <box background=”surface-secondary” radius=”lg” padding={3} align=”center” gap={1}> <title size=”lg”>User Mode</title> <text textAlign=”center” size=”sm”>Applications, browsers, games, and ordinary processes</text> <caption>Restricted access to hardware and protected system resources</caption> </box> <box align=”center” gap={1}> <icon name=”arrow-down-up” size=”2xl”/> <text textAlign=”center” weight=”medium”>System calls</text> <caption textAlign=”center”>Controlled requests for operating system services</caption> </box> <box background=”surface” border radius=”lg” padding={3} align=”center” gap={1}> <title size=”lg”>Kernel Mode</title> <text textAlign=”center” size=”sm”>Scheduling, memory management, drivers, and core operating system services</text> <caption>Privileged access to protected system resources</caption> </box> <box align=”center” gap={1}> <icon name=”arrow-down” size=”lg”/> <text weight=”medium”>Hardware interaction</text> </box> <grid columns={3} gap={2}> <grid-item> <box border radius=”md” padding={2} align=”center” gap={1}> <icon name=”cpu” size=”xl”/> <text weight=”medium” textAlign=”center” size=”sm”>CPU</text> </box> </grid-item> <grid-item> <box border radius=”md” padding={2} align=”center” gap={1}> <icon name=”memory-stick” size=”xl”/> <text weight=”medium” textAlign=”center” size=”sm”>Memory</text> </box> </grid-item> <grid-item> <box border radius=”md” padding={2} align=”center” gap={1}> <icon name=”hard-drive” size=”xl”/> <text weight=”medium” textAlign=”center” size=”sm”>Devices</text> </box> </grid-item> </grid> </box>
User mode is where ordinary applications execute with limited privileges. A program cannot normally access arbitrary physical memory or issue privileged processor instructions directly.
Kernel mode is where the operating system executes its most privileged code. The kernel can manage hardware resources and perform operations that applications are not permitted to perform independently.
When an application needs a protected service, it makes a system call. The processor transfers control to the appropriate kernel entry point, the kernel validates the request and performs the necessary work, and the result is returned to the application.
This separation improves security and system stability, although it cannot eliminate every vulnerability.
1. Monolithic Kernel Architecture
<AsyncImage query=”monolithic operating system kernel architecture diagram kernel services device drivers file system memory management” aspectRatio=”16:9″ width=”100%”/>
A monolithic kernel places many core operating system services within a single privileged kernel address space.
These services commonly include process scheduling, memory management, filesystem implementations, networking components, and device drivers.
Because many components execute within the same privileged environment, they can communicate directly through internal kernel interfaces without always requiring communication between separate protected services.
How It Works
Imagine that an application requests information from a storage device.
The request passes through the operating system’s file and storage layers. The relevant kernel components coordinate the request with the device driver, which communicates with the hardware.
In a monolithic design, many of these components reside within the same kernel space. This can reduce communication overhead and allow efficient interaction between services.
Advantages of Monolithic Kernels
- Performance: Direct communication between kernel components can reduce overhead.
- Efficient resource management: Core services can coordinate closely.
- Mature implementations: Monolithic kernels can support extensive hardware and software ecosystems.
- Flexible modularity: Some monolithic kernels allow supported components and drivers to be loaded as modules when needed.
Disadvantages of Monolithic Kernels
The main concern is that many components share a privileged environment.
A serious bug in a kernel-mode driver can potentially crash the entire system or compromise its security. A larger privileged codebase can also increase the complexity of auditing and maintaining the kernel.
Modularity can reduce the need to include every component in the initial kernel image, but loading a module does not automatically isolate it from the rest of the kernel.
Examples
- Linux uses a monolithic kernel architecture with support for loadable kernel modules.
- Traditional Unix systems have commonly used monolithic kernel designs.
Where Are Monolithic Kernels Useful?
Monolithic kernels are suitable for general-purpose systems that need broad hardware support, efficient resource management, and extensive networking and filesystem capabilities.
Linux’s kernel architecture has helped it serve a wide range of environments, from personal computers and servers to embedded devices and supercomputers.
2. Microkernel Architecture
<AsyncImage query=”microkernel operating system architecture diagram user space servers minimal kernel hardware” aspectRatio=”16:9″ width=”100%”/>
A microkernel takes a different approach by keeping the kernel itself relatively small.
Instead of placing many operating system services inside privileged kernel space, a microkernel typically keeps only essential mechanisms there. These may include basic scheduling, low-level memory management, and interprocess communication.
Other services, such as device drivers, filesystems, or networking components, may operate as separate processes outside the kernel, depending on the implementation.
How It Works
Suppose a storage service encounters a problem.
In a microkernel-based system, that service may run as a separate process with its own protected memory space. If the service fails, the architecture may allow it to be restarted without bringing down the entire operating system.
The precise recovery capabilities depend on the design and the service involved. A failure in a critical component or a kernel defect can still cause a system-wide failure.
Advantages of Microkernels
- Isolation: Separate services can run in protected address spaces.
- Potentially improved fault containment: Some service failures can be handled without crashing the whole system.
- Smaller privileged codebase: A smaller kernel can make security review and verification more manageable.
- Modularity: Services can sometimes be replaced or restarted independently.
- Suitability for specialized systems: Some microkernels are designed for high-assurance or safety-critical applications.
Disadvantages of Microkernels
Separating services can introduce communication overhead because components may need to exchange messages across process boundaries.
The architecture can also be more complicated to implement efficiently. Developers must carefully manage communication, synchronization, and service dependencies.
Modern microkernels can be highly optimized, so it is inaccurate to assume that every microkernel is inherently slow.
Examples
- MINIX 3.
- QNX Neutrino.
- seL4, a microkernel designed with formal verification and high-assurance use cases in mind.
Where Are Microkernels Useful?
Microkernels are particularly relevant to embedded systems, industrial applications, and environments where isolation and predictable behavior are important.
For example, automotive control systems and other safety-critical applications may benefit from architectures that limit the consequences of individual component failures.
3. Hybrid Kernel Architecture
<AsyncImage query=”hybrid operating system kernel architecture diagram Windows macOS kernel drivers services” aspectRatio=”16:9″ width=”100%”/>
A hybrid kernel combines characteristics associated with monolithic kernels and microkernels.
The aim is to balance efficient communication between core components with some degree of modularity and separation.
In practice, hybrid kernels often retain many services and drivers in privileged kernel space while adopting selected structural ideas from microkernel designs.
The term is useful for describing architectural choices, although operating systems do not always fit neatly into a single category.
How It Works
A hybrid kernel may place scheduling, memory management, and many drivers within the privileged kernel while organizing other components through modular interfaces or separate subsystems.
This can provide efficient communication for performance-sensitive operations while allowing the system to maintain a structured internal design.
Advantages of Hybrid Kernels
- Performance: Many important operations can occur within privileged kernel space.
- Architectural flexibility: Developers can organize the operating system into distinct subsystems.
- Broad hardware support: Kernel-integrated drivers can support a wide range of devices.
- Practical balance: The design can combine performance considerations with modular organization.
Disadvantages of Hybrid Kernels
- Complexity: Multiple architectural approaches can make the internal design difficult to understand and maintain.
- Privileged code exposure: Many drivers and services may still execute with high privileges.
- Fault propagation: A serious kernel-mode component failure can still affect the entire system.
Calling a kernel hybrid does not automatically make it more secure or faster than other architectures. Implementation quality, driver design, testing, and security controls remain essential.
Examples
- Windows NT uses a hybrid architecture.
- Apple’s XNU kernel, used in macOS and related Apple operating systems, combines Mach-derived components with BSD functionality and an I/O Kit driver framework.
Where Are Hybrid Kernels Useful?
Hybrid designs are common in general-purpose operating systems that must support complex hardware, application compatibility, and demanding performance requirements.
They can be effective when an operating system needs to balance practical engineering constraints across desktop, workstation, and other computing environments.
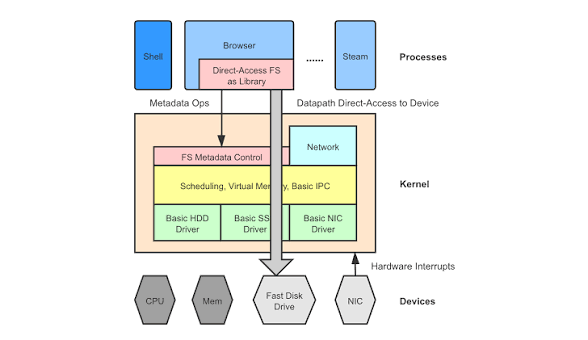
4. Exokernel Architecture
<AsyncImage query=”exokernel operating system architecture hardware protection library operating systems applications diagram” aspectRatio=”16:9″ width=”100%”/>
An exokernel is a more specialized architectural approach that aims to minimize the abstractions imposed by the operating system.
Rather than providing a large collection of traditional high-level resource abstractions directly through the kernel, an exokernel focuses on securely allocating and protecting physical resources.
Applications or library operating systems can then implement abstractions that suit their individual needs.
How It Works
In a traditional operating system, the kernel typically provides established abstractions for files, virtual memory, and other resources.
An exokernel instead aims to let applications or associated libraries manage certain resources more directly, while the kernel enforces protection and ownership rules.
This can provide greater flexibility for specialized applications that need unusual control over hardware resources.
Advantages of Exokernels
- Customization: Applications can use resource-management strategies suited to their needs.
- Potential efficiency: Specialized applications may avoid unnecessary abstractions.
- Resource control: Developers can experiment with different approaches to managing hardware.
Disadvantages of Exokernels
- Development complexity: Applications may need additional software layers.
- Limited mainstream adoption: Exokernels are not common in everyday consumer operating systems.
- Greater responsibility for developers: Custom resource management can create additional implementation and maintenance challenges.
Examples
MIT’s Exokernel project is a well-known research example of this architecture.
Where Are Exokernels Useful?
Exokernels are primarily important in research and specialized system design, where developers investigate how direct resource control might improve performance or flexibility.
For ordinary desktop users, an exokernel is much less likely to be a practical choice than a mainstream operating system.
Kernel Architecture Comparison
| Feature | Monolithic | Microkernel | Hybrid | Exokernel |
|---|---|---|---|---|
| Kernel structure | Many core services in kernel space | Minimal core, more services outside it | Mix of architectural approaches | Minimal resource-protection layer |
| Communication overhead | Often relatively low internally | Can involve additional message passing | Depends on subsystem design | Depends on libraries and resource-management design |
| Fault isolation | Limited between many kernel components | Often stronger between separated services | Varies by implementation | Depends on surrounding system design |
| Implementation complexity | Can be substantial | Substantial communication and service-management complexity | Substantial architectural complexity | High for application and library developers |
| Common use | General-purpose systems | Specialized, embedded, and high-assurance systems | General-purpose operating systems | Research and specialized systems |
No architecture is universally best. The right choice depends on the system’s priorities, including performance, reliability, security, hardware compatibility, and development cost.
How the Kernel Manages the CPU
The processor executes instructions, but it cannot independently decide how all applications should share its resources. The operating system’s scheduler plays a central role in that process.
Process and Thread Scheduling
A process is an executing program together with its associated resources. A thread is an execution path within a process.
Modern operating systems commonly schedule threads, allowing multiple programs to make progress even when the machine has fewer CPU cores than runnable threads.
The kernel determines which runnable thread should execute, taking into account factors such as scheduling policy, priority, processor availability, and system responsiveness.
For example, while you listen to music and browse the web, the scheduler allocates processor time among browser activity, audio processing, and background services.
On multicore systems, the kernel can also distribute work across multiple CPU cores.
Context Switching
When the processor stops executing one thread and begins executing another, the operating system may need to save and restore relevant execution state.
This process is called a context switch.
Context switching allows a computer to share processor resources among many tasks, although it introduces some overhead.
An effective scheduler attempts to balance responsiveness, fairness, throughput, and the needs of time-sensitive workloads.
Handling Interrupts
Hardware devices sometimes need the processor’s attention.
A network adapter may signal that data has arrived, or a storage controller may indicate that an operation has completed.
These signals can trigger interrupts, allowing the operating system to respond to hardware events.
The kernel and relevant drivers process these events, coordinate any necessary work, and allow applications to receive the results.
How the Kernel Manages Memory
Memory management is another essential responsibility of the kernel.
Each running application needs memory for instructions, data, temporary calculations, and other information. If applications could access one another’s memory without restrictions, a programming error or malicious process could corrupt sensitive data.
The kernel works with hardware memory-management features to create protected memory spaces and control access.
Virtual Memory
Most modern operating systems provide each process with a virtual address space.
Virtual memory allows a process to use addresses that are mapped to physical memory or, under appropriate circumstances, to other backing storage.
This abstraction helps isolate processes and makes memory allocation more flexible.
For example, a browser and a text editor can use similar virtual address ranges without normally accessing the same physical memory.
Memory Allocation
When an application requests memory, the operating system arranges for the required memory resources to be made available.
The kernel also tracks which memory regions are in use, enforces protection rules, and manages the release of resources when they are no longer needed.
Paging and Memory Pressure
When physical RAM becomes scarce, operating systems may reclaim memory, compress selected memory contents, or move certain data to backing storage.
These techniques can allow a computer to continue operating when its active memory requirements exceed available physical RAM, but they can also reduce performance.
Storage is generally much slower than RAM, so excessive paging can make a computer feel unresponsive.
This is one reason why adequate memory and efficient resource management matter on older computers.
How the Kernel Communicates With Hardware
A computer contains many different hardware components, each with its own capabilities and communication requirements.
The kernel coordinates access to these devices through device drivers and related subsystems.
What Is a Device Driver?
A device driver is software that enables the operating system to communicate with a particular class of hardware or device interface.
Drivers may support graphics adapters, network interfaces, storage controllers, USB devices, audio hardware, and many other components.
When an application plays a video, for example, the operating system and relevant drivers coordinate access to graphics and audio hardware as required.
The application usually does not need to know the low-level details of each device.
Why Drivers Matter
A well-designed driver helps the operating system use hardware correctly and efficiently.
However, drivers can also introduce compatibility and security problems. A buggy driver may cause crashes, while a vulnerable driver with elevated privileges may provide attackers with a way to gain additional control.
For this reason, keeping drivers updated through trusted sources is an important part of system maintenance.
On systems where drivers run in kernel space, their failures can have particularly serious consequences. Some operating systems and device frameworks provide mechanisms to move selected driver functions into more isolated environments.
System Calls: The Bridge Between Applications and the Kernel
Applications need access to operating system services, but they cannot safely perform every privileged operation directly.
System calls provide a controlled interface through which applications request these services.
Common examples include operations related to:
- Opening, reading, and writing files.
- Creating processes and managing execution.
- Allocating or mapping memory.
- Communicating through network sockets.
- Accessing selected device functions.
- Obtaining system information.
Consider what happens when you save a document.
The application prepares the data and requests a file operation through an operating system interface. The kernel validates the request and coordinates with the filesystem and storage layers. Depending on caching, hardware, and filesystem behavior, the data may be written immediately or at a later stage.
The application receives a result indicating whether the operation succeeded or failed.
System calls provide an important security boundary because the kernel can check permissions and validate requests before allowing protected operations to proceed.
The Kernel’s Role in Operating System Security
Kernel architecture has a direct influence on security because the kernel manages access to important system resources.
A vulnerability in a privileged kernel component can have more serious consequences than a vulnerability confined to an ordinary application.
Privilege Separation
Separating user-mode applications from privileged kernel code limits what an ordinary process can do directly.
This design can help prevent a compromised application from immediately obtaining unrestricted access to the system.
However, attackers may still exploit kernel vulnerabilities or abuse legitimate system interfaces if appropriate protections are missing.
Access Control
The operating system checks permissions when processes attempt to access protected resources.
Depending on the platform, controls may include file permissions, process isolation, security policies, capabilities, and other mechanisms.
The kernel enforces many of these restrictions, while higher-level services and frameworks may contribute additional checks.
Kernel Updates
Security vulnerabilities can affect memory management, device drivers, networking, filesystems, and other privileged components.
Operating system updates often include patches for such problems.
Installing updates from official and trusted sources helps reduce exposure to known vulnerabilities.
Secure Boot and Kernel Integrity
Secure Boot can help establish a chain of trust during system startup by checking the authenticity of selected boot components.
Some operating systems also support kernel code-integrity checks and other mechanisms intended to prevent unauthorized modifications to privileged code.
The details vary across platforms, and these technologies do not eliminate every possible attack.
What Happens When the Kernel Crashes?
A kernel failure can interrupt the entire operating system because the kernel manages essential system functions.
The visible result depends on the operating system and the nature of the failure.
On Windows, a serious kernel-mode failure can produce a stop error, commonly known as a blue screen.
On Linux, a severe kernel failure may result in a kernel panic.
On macOS, a serious system-level failure can result in a kernel panic and restart.
Common Causes
Kernel crashes can be caused by several issues:
- Faulty or incompatible device drivers.
- Defective or unstable hardware.
- Memory errors.
- Kernel bugs or unsupported configurations.
- Certain low-level software conflicts.
- Overheating or unstable power conditions in some circumstances.
How to Reduce the Risk
Keep the operating system and drivers updated, avoid untrusted low-level software, and monitor recurring crashes.
If a system begins crashing after a driver or software change, investigate that change and follow the operating system’s troubleshooting guidance.
Hardware diagnostics may also be necessary if crashes continue.
A single crash does not automatically mean that the kernel architecture is poorly designed. Reliability depends on many factors, including implementation quality, hardware behavior, and software compatibility.
How Different Operating Systems Use Kernel Architecture
Different operating systems make different architectural choices based on their goals and historical development.
Linux
Linux uses a monolithic kernel with loadable modules.
Many services and drivers operate in kernel space, while modules allow supported functionality to be added or removed without rebuilding the entire kernel image.
This design supports a wide range of hardware and workloads, from small embedded devices to large servers.
Windows
Windows uses the Windows NT architecture, commonly described as hybrid.
Its kernel architecture includes privileged components such as the kernel and executive, alongside user-mode services and applications. Drivers and other components have defined interfaces for interacting with the operating system.
The design supports broad hardware compatibility, application support, and extensive system-management capabilities.
macOS
macOS uses XNU, a hybrid kernel that combines Mach-derived functionality, BSD components, and Apple’s I/O Kit framework.
This architecture supports process and memory management, networking, device interaction, and other operating system services.
Apple also combines kernel-level mechanisms with higher-level platform security technologies.
Why These Differences Matter
Kernel architecture influences how an operating system organizes its services, manages failures, and allows components to communicate.
However, the architecture alone does not determine which operating system is fastest or most secure.
Hardware, driver quality, security updates, system configuration, and application workloads all influence the final user experience.
The Future of Kernel Architecture
Kernel development continues to evolve as computers become more interconnected and hardware grows more specialized.
Several trends are influencing the way operating systems manage resources.
1. Stronger Isolation and Security
Modern operating systems increasingly rely on sandboxing, privilege separation, memory protection, and other techniques to limit the consequences of software vulnerabilities.
Kernel architecture remains important because the privileged components form a critical part of the system’s security foundation.
2. Support for Specialized Hardware
Graphics processors, AI accelerators, high-speed networking devices, and other specialized components introduce new resource-management requirements.
Operating systems must coordinate these devices efficiently while maintaining appropriate protection and compatibility.
3. Virtualization and Cloud Computing
Virtual machines allow multiple operating system instances to share physical hardware through a virtualization layer.
The kernel plays an important role in scheduling workloads, managing memory, and supporting the interfaces required by virtualization technologies.
Container technologies also rely on operating system features that isolate processes and control resource usage. On Linux, for example, namespaces and control groups provide important foundations for containers.
4. Real-Time and Embedded Systems
Some applications require predictable response times rather than maximum overall throughput.
Industrial controllers, robotics, and certain automotive systems may need operating systems that can respond to events within defined timing constraints.
Kernel scheduling policies, interrupt handling, and system design become particularly important in these environments.
5. Better Reliability Through Verification and Testing
As software systems become more complex, developers continue exploring ways to improve confidence in critical kernel components.
Techniques such as extensive automated testing, static analysis, fuzzing, and formal verification can help detect defects and strengthen reliability.
These approaches require investment and do not guarantee the absence of vulnerabilities, but they can improve the quality of important system components.
Conclusion
Kernel architecture is one of the foundations of modern computing. It determines how an operating system organizes privileged services, communicates with hardware, allocates resources, and protects applications from one another.
Monolithic kernels offer efficient communication between many core components, microkernels emphasize a small privileged core and stronger service isolation, hybrid kernels combine architectural approaches, and exokernels explore more direct resource management for specialized applications.
Each design has its own advantages and trade-offs. There is no universally perfect architecture, because different systems must balance performance, security, reliability, compatibility, and complexity.
The kernel also performs many essential tasks that users rarely notice. It schedules processor time, manages virtual memory, coordinates device drivers, processes system calls, and enforces important security boundaries.
As computing continues to evolve, kernel architecture will remain central to operating system development. From cloud infrastructure and embedded devices to personal computers and AI-enabled systems, the kernel provides the mechanisms that allow software and hardware to work together.
Understanding how it operates offers a clearer picture of what happens beneath the desktop interface and why operating system design matters to the performance, stability, and security of every modern computer.